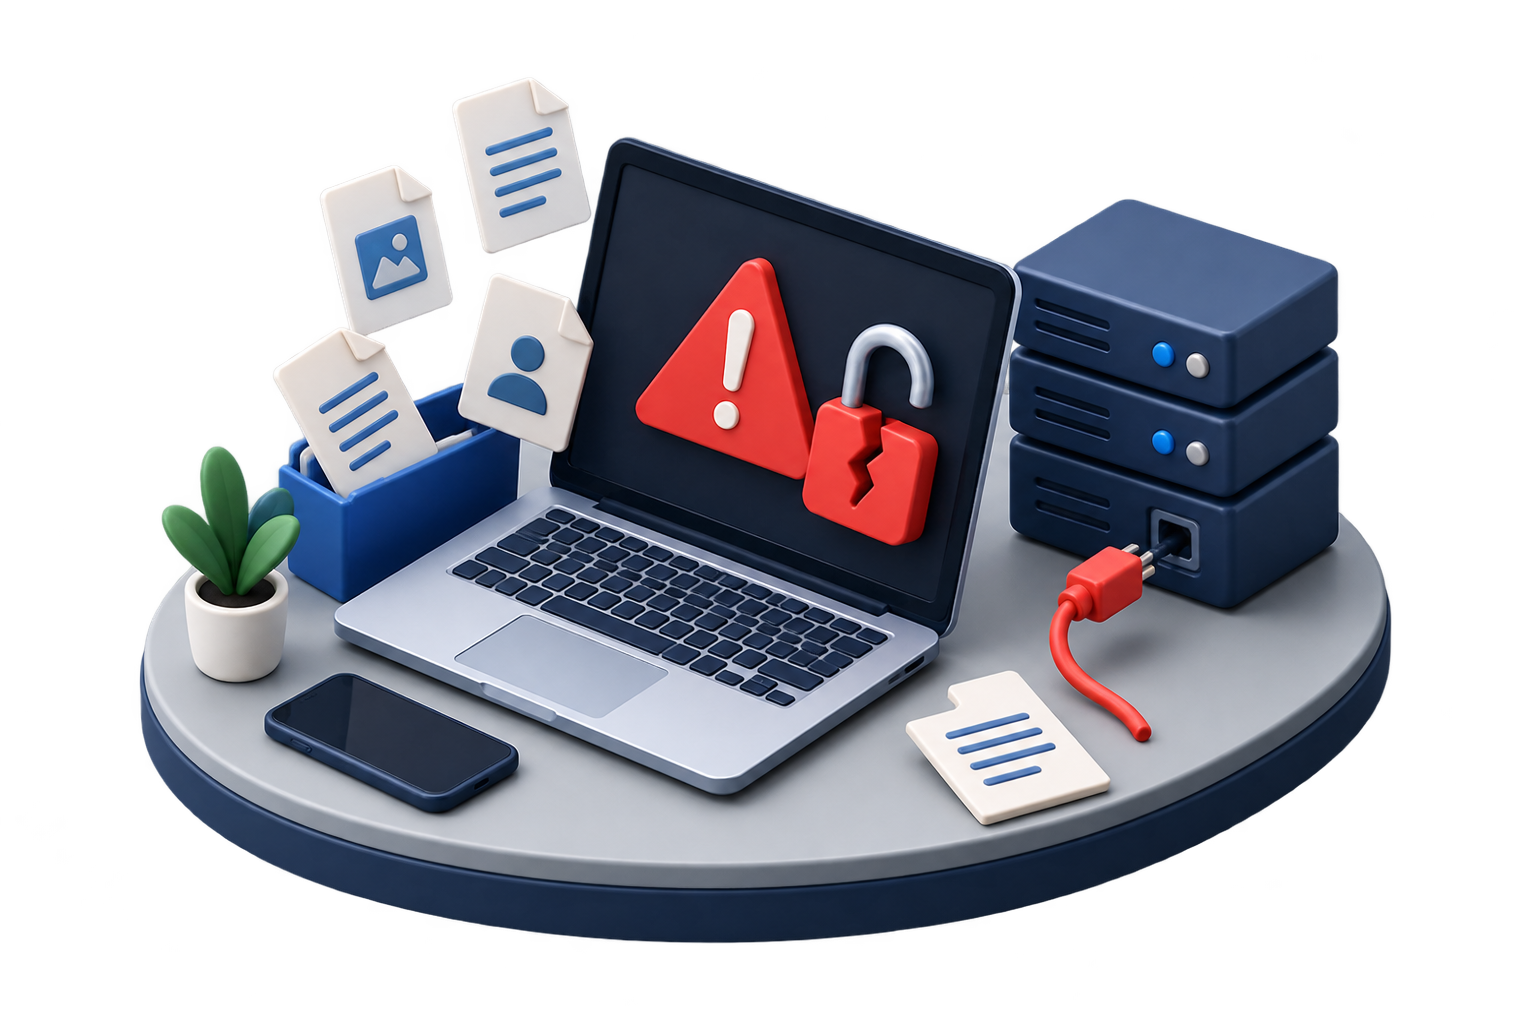
A business account is compromised
Scenario: An attacker gains access to a business email account.
What happens next: Contact the approved incident-response channel promptly. Preserve evidence and follow policy notification requirements.
Incident response and liability to others should be compared separately.
Data types, systems, backups, access controls and service providers.
Which response costs and third-party claims are included, and who must be contacted?
Start my business enquiry →Hypothetical situation
A security incident interrupts access to business systems.
Ask which wording, conditions and notification requirements would apply. A scenario does not establish coverage or guarantee an outcome.
Covers breach response, third-party liability, ransomware, business interruption from a cyber event, and privacy regulatory exposure.

 A.M. Fredericks UnderwritingABEX o/b Affiliated Broker Exchange
 Allianz Global RisksAmbri AssuranceApril Canada Inc.April MarineArthur J. Gallagher & Co
 AVRO Insurance ManagersBeazley Canada LimitedBerkley Insurance CompanyBlueCross BlueShield
 Burns & Wilcox CanadaCAA InsuranceCAN - Continental Insurance
 Cansure Underwriting LtdCaradoc Townsend MutualChes Special Risk Inc.Chubb InsuranceChutter Underwriting Services
 Core Underwriting ServicesDefinityDesjardins Financial Security Investments Inc.
 Dominion of Canada/Travelers/Travelers EssentialEagle Underwriting Group Inc.Echelon
 Excess Underwriting Corp.Facility Association
 Forward InsuranceGlobal Aerospace Underwriting
 Great-West LifeGroupAssureGroupOne Insurance
 HDI Global Specialty SE
 IA Excellence Life Insurance
 INGLE International
 Intact Public Entities
 La CapitaleLiberty International CanadaLynx Insurance UnderwritersMarkel
 NorthbridgeOld Republic
 Optiom
 PAL Insurance Brokers Canada
 Premier Canada AssurancePremier MarinePremium Marine
 Revolution Advanced Underwriting
 SignalSignature Risks
 South Western GroupSovereign GeneralSpecial Risk InsuranceSports & Fitness InsuranceSSQ AssuranceStarr Technical RisksStrategic UnderwritingSummit Underwriting Group Inc.The Boiler Inspection and Indemnity Company (BI&I)
 The Totten Insurance GroupTrans Canada
 TravelersTrinity Underwriting
 Unique Risks
 Victor Insurance
From Insurance Genie
Explore recent policy purchases shared through our participating insurance professionals.
Recent policies will appear here when the Insurance Genie CRM feed is connected.
Anyone holding personal information or dependent on systems to trade. In practice, everyone.
It does not fix bad controls. Insurers increasingly decline rather than rate for missing multi-factor authentication.
PIPEDA and provincial privacy statutes drive the Canadian regulatory piece, not US state breach-notification law. Quebec’s Law 25 adds obligations the US framing misses entirely.
| Canonical name | Cyber Liability |
|---|---|
| Abbreviation | Cyber |
| How it is bought | Standalone |
| Category | Liability |
| Typical limits | Range only, with the basis stated — Canada publishes no commercial tariff |
Limits are written to the exposure and to what your contracts demand, not to a rule of thumb. Any page quoting a single “standard” limit for a class of business is quoting one broker’s habit.
One request, and someone licensed to place this coverage picks it up.
Be prepared
Hypothetical situations to help you prepare questions—not actual client claims or promises of coverage.
Scenario: An attacker gains access to a business email account.
What happens next: Contact the approved incident-response channel promptly. Preserve evidence and follow policy notification requirements.
Scenario: A malicious incident interrupts access to business systems.
What happens next: Document the interruption and recovery costs. The insurer checks the trigger, waiting periods and selected cyber benefits.
Scenario: The business discovers possible unauthorized access to customer information.
What happens next: Seek appropriate incident-response and legal guidance. Notification duties and insurance response require separate assessment.
Actual outcomes depend on the facts and applicable wording. Read claims guidance · Ask about the next step
Hi, I’m Genie. I can explain how this website works, help you find a page, or point you to a person. I can’t answer coverage questions or give insurance advice.